About the role
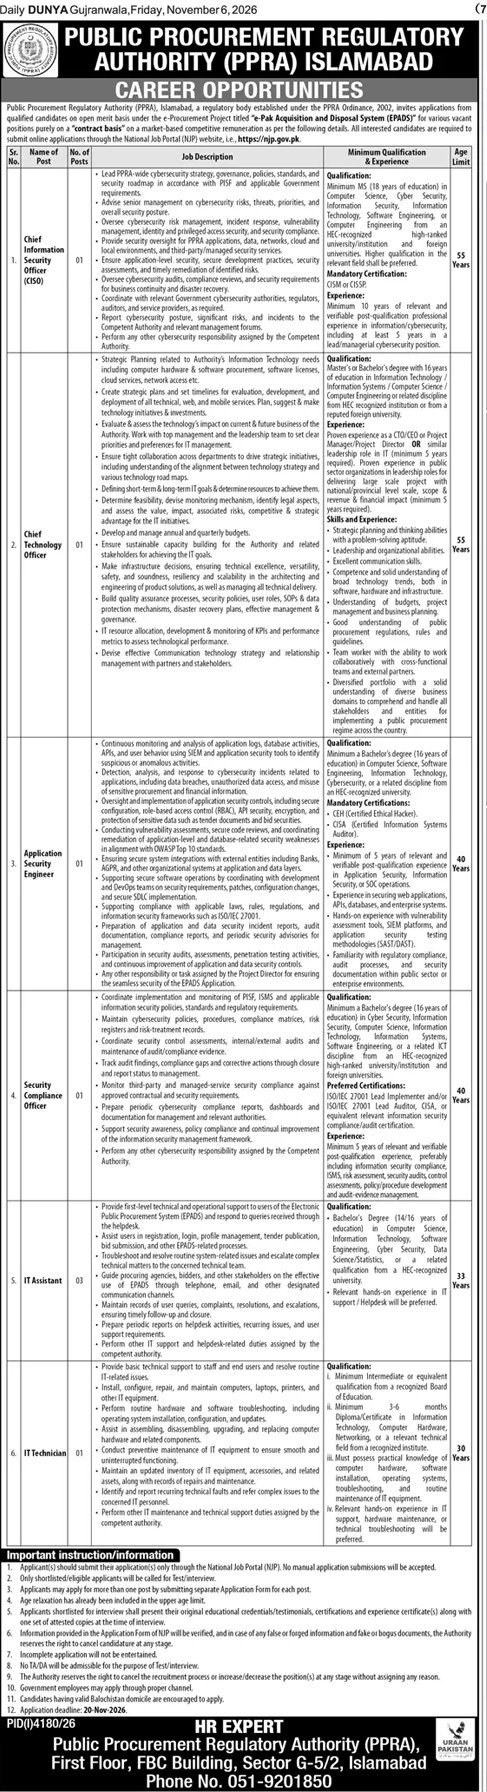
The Public Procurement Regulatory Authority (PPRA), Islamabad, is a regulatory body established under the PPRA Ordinance, 2002. It invites applications from qualified candidates on an open-merit basis for its e-Procurement Project, the e-Pak Acquisition and Disposal System (EPADS). These positions are purely on a contract basis, with market-based competitive remuneration.
The advertised responsibilities are as follows:
Chief Information Security Officer (CISO): Lead PPRA-wide cybersecurity strategy, governance, policies, standards and the security roadmap in accordance with PPISF and applicable government requirements. Advise senior management on cybersecurity risks, threats, priorities and security posture. Oversee cybersecurity risk management, incident response, vulnerability management, identity and privileged-access security, and compliance. Provide security oversight for applications, data, networks, cloud and local environments, and third-party or managed security services. Ensure application-level security, secure development practices, security assessments and timely remediation. Oversee cybersecurity audits, compliance reviews and business-continuity and disaster-recovery security requirements. Coordinate with relevant government cybersecurity authorities, regulators, auditors and service providers. Report cybersecurity posture, significant risks and incidents to the competent authority and relevant management forums, and perform other assigned cybersecurity responsibilities.
Chief Technology Officer: Lead strategic planning for the authority's information technology needs, including hardware, software procurement, software licences, cloud services and network access. Develop strategic plans and timelines for evaluating, developing and deploying technical, web and mobile services, and suggest improvements and investments. Evaluate technology's effect on current and future business and work with management to establish leadership preferences for IT management. Align departments with technology strategy, understand business needs and define short- and long-term IT goals. Determine feasibility, monitoring mechanisms, legal aspects and assets, and ensure innovative, cost-effective IT strategies. Manage annual and quarterly budgets, build sustainable technical capacity, resolve weaknesses, and make outsourcing or talent decisions. Provide infrastructure and operational guidance covering security, reliability, sourcing, resiliency and scalability. Build quality-assurance processes, security policies, standards, operating procedures, disaster-recovery plans and governance. Oversee KPIs, performance metrics, communication technology strategy and stakeholder relationships.
Application Security Engineer: Continuously monitor and analyse application logs, database activity, APIs and user behaviour using SIEM and application-security tools. Detect, analyse and respond to cybersecurity incidents involving data breaches, unauthorized access and sensitive-data misuse. Oversee role-based access control, API security, encryption and sensitive-data protection. Conduct vulnerability assessments, secure-code reviews and remediation of application and database weaknesses in alignment with the OWASP Top 10. Integrate security testing with external entities, including banks, APGR and other organizational systems at application and data layers. Support secure software operations with development and DevOps teams through code reviews, patches, configuration changes and secure SDLC implementation. Support compliance with relevant laws and information-security frameworks, including ISO/IEC 27001. Prepare incident reports, audit documentation, compliance reports and periodic security advisories. Participate in audits, assessments, penetration testing and continuous security improvement, and perform other assigned tasks to maintain EPADS security.
Security Compliance Officer: Coordinate implementation and monitoring of PPISF, ISMS and applicable information-security policies, standards and regulatory requirements. Maintain cybersecurity policies, procedures, compliance matrices, risk registers and risk-treatment records. Coordinate control assessments, internal and external audits, and compliance evidence. Track findings, compliance gaps and corrective actions through closure, and report status to management. Monitor third-party and managed-service compliance against approved requirements. Prepare periodic compliance reports, dashboards and documentation. Support security awareness, policy compliance and continuous improvement of the information-security management framework, and perform other assigned cybersecurity responsibilities.
IT Assistant: Provide first-level technical and operational support to EPADS users through the helpdesk. Assist with registration, login, profile management, tender publication, bid submission and other EPADS processes. Troubleshoot routine system issues and escalate complex matters to the technical team. Guide procuring agencies, bidders and other stakeholders through telephone, email and other designated channels. Maintain user queries, complaints, resolutions and escalations with timely follow-up and closure. Prepare periodic helpdesk activity reports, record recurring issues and suggest improvements. Perform other assigned IT-support and helpdesk duties.
IT Technician: Provide basic technical support for staff and end users. Install, configure, repair and maintain computers, laptops, printers and other IT equipment. Troubleshoot hardware and software, including operating-system installation, configuration and updates. Assist with cabling, desktop setup, upgrades and replacement of hardware components. Conduct preventive maintenance, maintain equipment and spare-parts inventories, and record repairs and maintenance. Identify and report recurring faults, refer complex issues to the relevant IT personnel, and perform other assigned maintenance and support duties.
Posts and vacancies
| Post | Vacancies | Maximum age |
|---|
| Chief Information Security Officer (CISO) | 1 | 55 years |
| Chief Technology Officer | 1 | 55 years |
| Application Security Engineer | 1 | 35 years |
| Security Compliance Officer | 1 | 40 years |
| IT Assistant | 3 | 33 years |
| IT Technician | 1 | 30 years |
Eligibility
Chief Information Security Officer (CISO): Minimum MS, representing 18 years of education, in Computer Science, Cyber Security, Information Security, Information Technology, Software Engineering or Computer Engineering from an HEC-recognized, high-ranked university or institution, or a recognized foreign university. Higher qualifications in the relevant field are preferred. Mandatory certification: CISM or CISSP. At least 10 years of relevant and verifiable post-qualification professional experience in information security or cybersecurity, including at least five years in a lead or managerial cybersecurity position.
Chief Technology Officer: A master's or bachelor's degree with 16 years of education in Information Technology, Information Systems, Computer Science, Computer Engineering or a related discipline from an HEC-recognized institution or recognized foreign university. Proven experience as CTO, CEO, Project Manager, Project Director or in a similar IT leadership role, with at least five years required. Candidates must have proven leadership experience in public-sector organizations delivering large-scale projects with national or provincial scope and financial impact, with a minimum of five years required. Required capabilities include strategic planning, innovation, leadership, organization, communication, understanding of broad technology trends in software, hardware and infrastructure, budgets, project management, business planning, public procurement regulations and teamwork across cross-functional teams and external partners.
Application Security Engineer: Minimum bachelor's degree with 16 years of education in Computer Science, Software Engineering, Information Technology, Cybersecurity or a related discipline from an HEC-recognized university. Mandatory certifications: CEH (Certified Ethical Hacker) and CISA (Certified Information Systems Auditor). At least five years of relevant and verifiable post-qualification experience in application security, information security or security operations. Experience securing web applications, APIs, databases and enterprise systems is required, along with hands-on vulnerability assessment, SIEM platforms and application-security testing methodologies such as SAST and DAST. Familiarity with regulatory compliance, audit processes and security documentation in public-sector or enterprise environments is also required.
Security Compliance Officer: Minimum bachelor's degree with 16 years of education in Cyber Security, Information Security, Computer Science, Information Technology, Information Systems, Software Engineering or a related IT discipline from an HEC-recognized, high-ranked university or institution, or a recognized foreign university. Preferred certifications include ISO/IEC 27001 Lead Implementer and/or ISO/IEC 27001 Lead Auditor, CISA, or equivalent relevant information-security compliance or audit certification. At least five years of relevant and verifiable post-qualification experience, preferably in information-security compliance, ISMS, risk assessment, security audits, control assessments, policy or procedure development, and audit-evidence management.
IT Assistant: Bachelor's degree with 14 or 16 years of education in Computer Science, Information Technology, Software Engineering, Cyber Security, Data Science, Statistics or a related qualification from an HEC-recognized university. Relevant hands-on experience in IT support or helpdesk work is preferred.
IT Technician: Minimum Intermediate or equivalent qualification from a recognized board of education, or minimum three to six months' diploma or certificate in Information Technology, Computer Hardware, Networking or a relevant technical field from a recognized institute. Candidates must have practical knowledge of computer hardware, software installation, operating systems, troubleshooting and routine IT-equipment maintenance. Relevant hands-on experience in IT support, hardware maintenance or technical troubleshooting is preferred.
Age relaxation has already been included in the upper age limits. Candidates with a valid Balochistan domicile are encouraged to apply.
How to apply
Submit applications online through the National Job Portal at https://njp.gov.pk Manual applications will not be accepted. Applicants may apply for more than one post by submitting a separate application form for each position.
Only shortlisted eligible applicants will be called for a test or interview. Shortlisted applicants must present their original educational credentials, testimonials, certifications and experience certificates, together with one set of attested copies, at the interview.
Information supplied in the application will be verified. False or forged information or bogus documents may lead to cancellation of candidature at any stage. Incomplete applications will not be entertained. Government employees must apply through the proper channel. No TA/DA will be admissible for the test or interview.
The authority reserves the right to cancel the recruitment process or increase or decrease the number of positions at any stage without assigning a reason.
Contact: HR Expert, Public Procurement Regulatory Authority (PPRA), First Floor, FBC Building, Sector G-5/2, Islamabad. Phone: 051-9201850.
Important dates
Application deadline: 20 November 2026.
No comments yet. Start the conversation for this job.