About the role
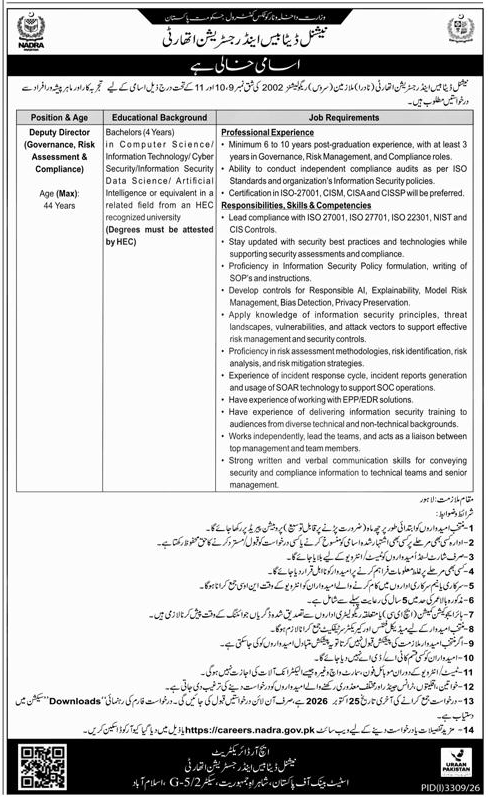
NADRA is seeking a Deputy Director for Information Security and Compliance. The role will lead and manage compliance with recognized security and privacy standards, support security assessments, and act as a liaison between senior management and technical teams. The successful candidate will prepare information security policies, write SOPs and instructions, develop controls for responsible AI and model risk management, and stay current with security best practices and technologies.
Responsibilities include leading compliance with ISO 27001, ISO 27701, ISO 22301, NIST and CIS Controls; conducting independent compliance audits; applying information security principles to risk management; performing risk identification, analysis and mitigation; supporting incident response including report generation and use of SOAR technology to support SOC operations; working with EPP/EDR solutions; and delivering information security training to diverse audiences.
Posts and vacancies
Eligibility
- Education: Bachelor's degree (4 years) in Computer Science, Information Security, Data Science / Artificial Intelligence or an equivalent field. Degrees must be attested by the Higher Education Commission (HEC).
- Experience: Minimum 6 to 10 years post‑graduate experience, with at least 3 years in Governance, Risk Management and Compliance roles.
- Certifications: Certification in ISO 27001, CISM, CISA or CISSP will be preferred.
- Skills: Proficiency in information security policy formulation, SOP writing, risk assessment methodologies, incident response processes, SOAR tools, EPP/EDR solutions, and the ability to develop controls for Responsible AI, explainability, model risk, bias detection and privacy preservation. Strong written and verbal communication and team leadership skills are required.
No comments yet. Start the conversation for this job.